Welcome!
Vintage Web 2.0 aesthetics,
snippets of code,
thoughts, photography,
and a bit of charm. History of the siteLinux
Everything that concerns. Go to categoryElectronics
micro, radio,
and usual. Go to categoryPhoto
From different categories. View category
- This is an original category in English «Linux»
- Читати цей розділ українською «Лінукс»
- Читать этот раздел на русском «Линукс»
Now sharing data with more than just Anthropic's servers
Everything about this story is beautiful.
A popular editor, Claude Code, and an SSH tunnel forwarded straight to your machine.
Why settle for just collecting data, right?
A compromise of the official Claude Code extension for VS Code, developed by Anthropic.
If you can lock something down - lock it down
8/October/2026 gitlabzero-trustztna
و ̑̑ GitLab Fall's CVE Hits /ᐠ。ꞈ。ᐟ\")
they_are_just_devops.png
I just remembered a funny chain of events.
Some time ago, a colleague texted me asking why our secondary GitLab server was not only restricted to outsiders, but also (without getting into too many details) had its front-end locked down with an auth_basic directive in Nginx?
I jokingly replied that if it was really making his life miserable, we could disable it for his pool of IPs, both work and home. Or he could just open it himself, since he’s a sysadmin too.
And that was that.
Literally a week later, a new Critical patch release drops.
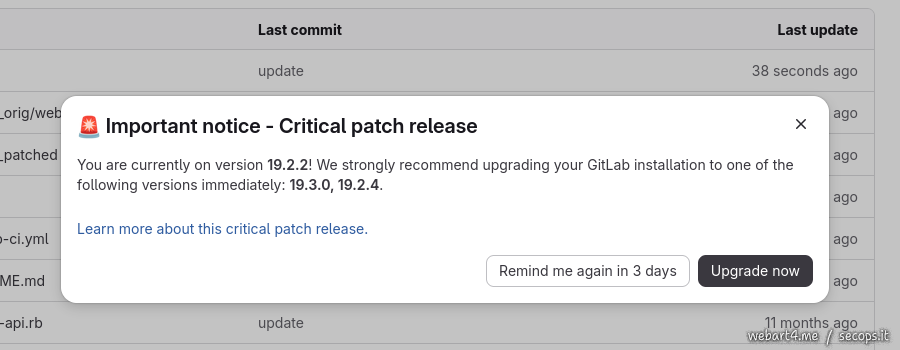
GitLab issues emergency patch: GitLab has issued an emergency patch for a critical vulnerability (CVE-2026-19478) with a severity score of 9.4 out of 10.
It put a smile on my face back then. A few days later, another alert arrives about a new critical update.
Configuring WireGuard on CentOS, Debian, Ubuntu, and FreeBSD in four different ways
7/August/2026 wireguardcentosdebianubuntufreebsd
Below is a set of snippets for configuring WireGuard for three different Linux distributions and FreeBSD.
The setup assumes a Debian server with a 10.9.21.0/24 network.
Server, Debian
apt install wireguard-tools
nano /etc/network/interfaces.d/wg0
umask 077
cd /etc/wireguard/
wg genkey > server-private.key
wg pubkey < server-private.key > server-public.key
nano /etc/wireguard/wg0.conf
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 | |
Compromise of 32 Red Hat packages in the NPM directory and 1,577 packages in the AUR repository
A good addition to the collection.
The news needs to be given time to settle, and then the details can be savored.
- Red Hat, RED HAT, CARL!
- GitHub Actions, as usual.
- NPM, we’re already used to it.
- Arch User Repository, it’s already more interesting.
Critical remote vulnerability in Nginx CVE-2026-9256
Let’s rebuild Nginx with CVE-2026-9256 patch according to the Debian-way.
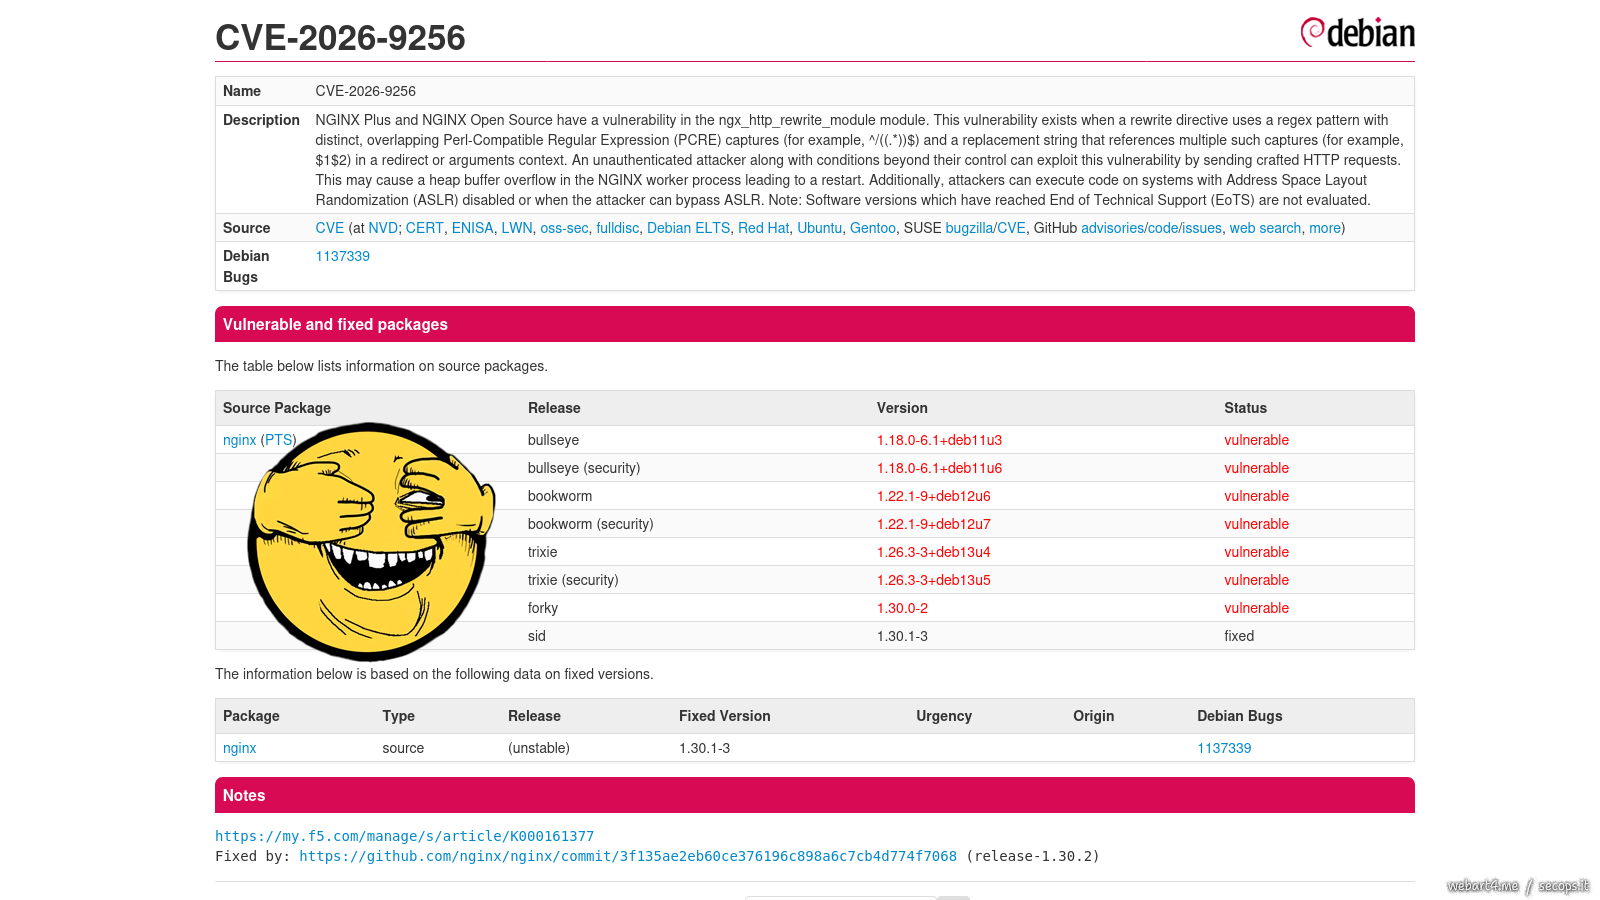
A critical vulnerability in nginx allows remote code execution with the privileges of the nginx worker process by sending a specially crafted HTTP request.
But that’s not the point.
The problem is that Debian maintainers are in no hurry to release a new patch package.
nano /etc/apt/sources.list
1 2 3 4 | |